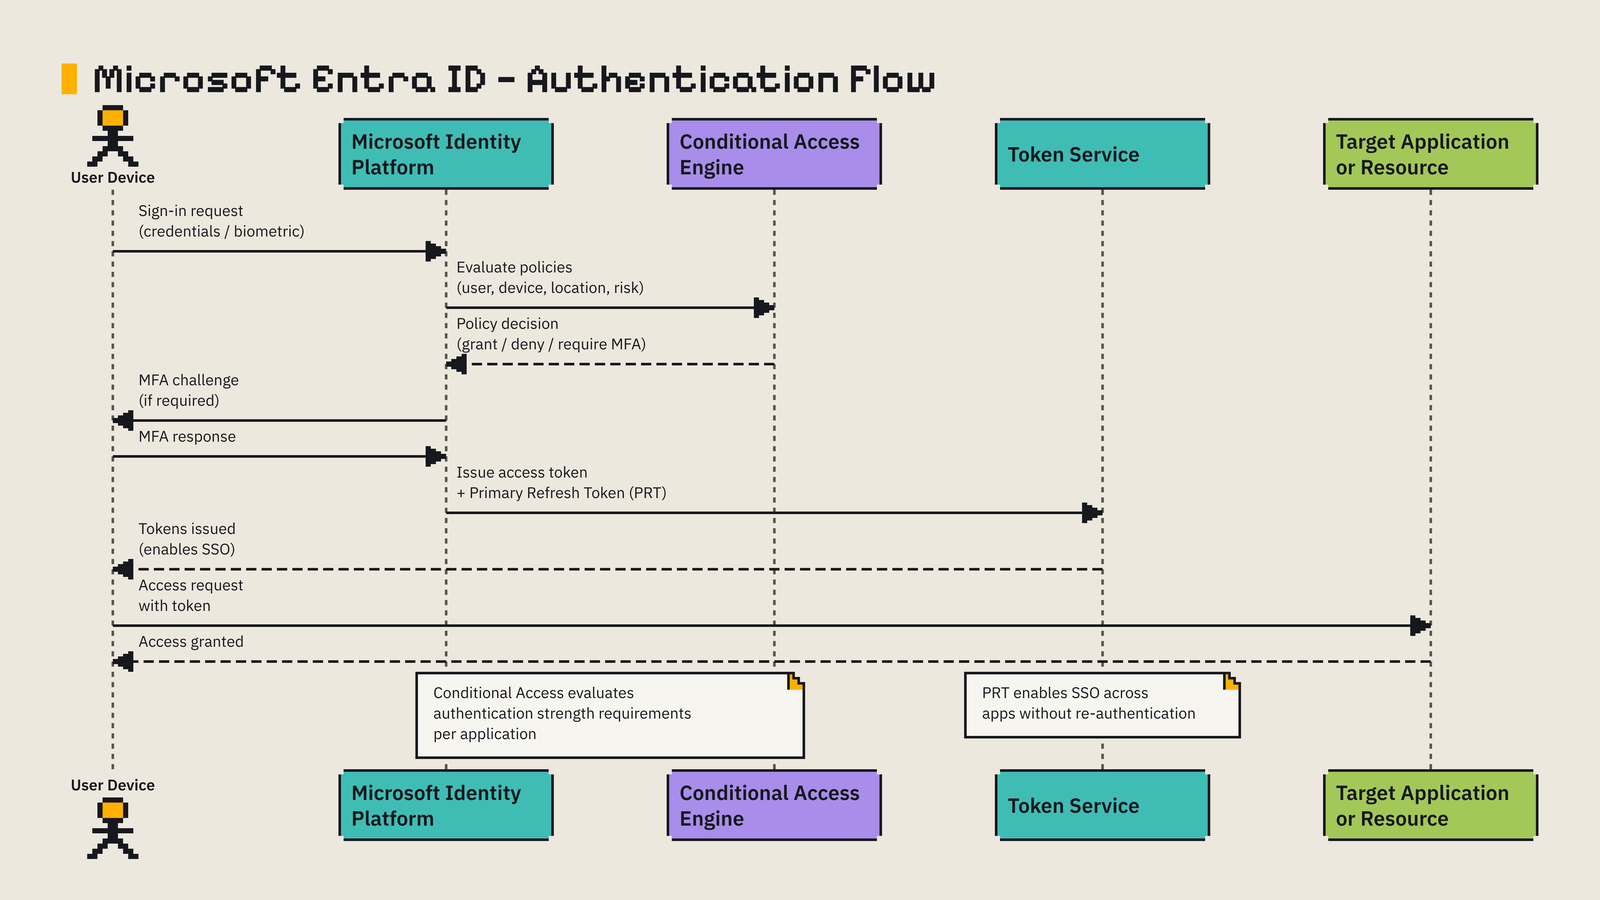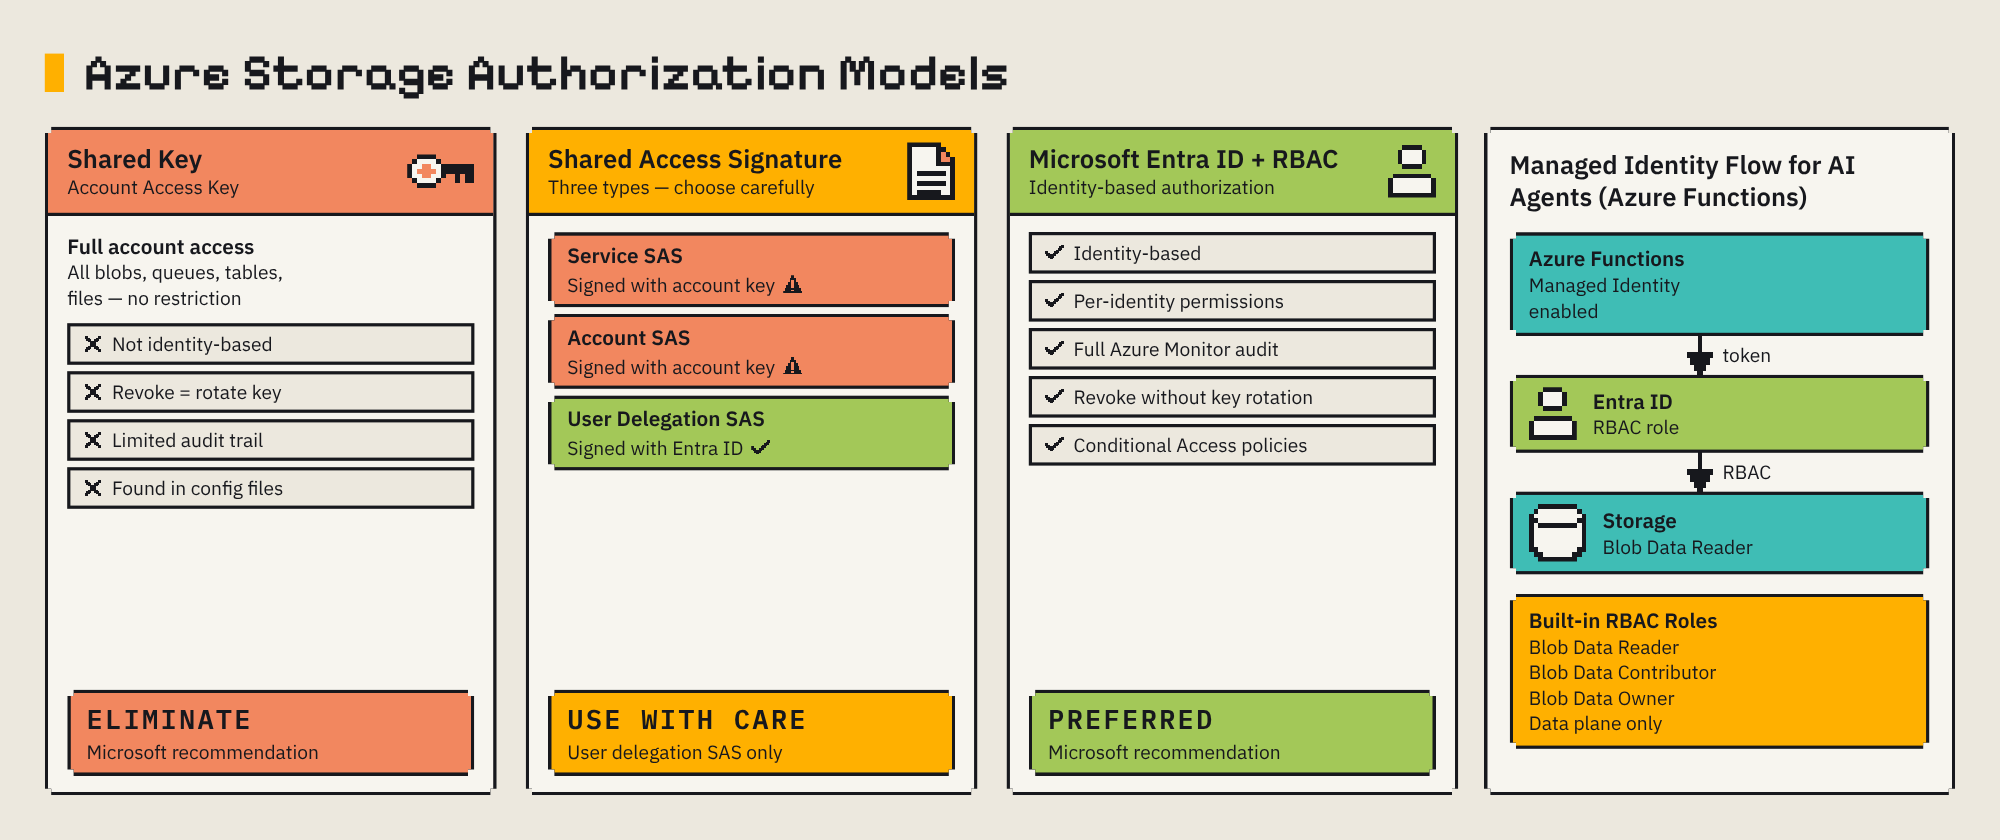
Comparison of Azure Storage authorization models: Shared Key, service and account SAS, user delegation SAS, and Microsoft Entra ID with RBAC. A flow diagram shows Azure Functions accessing Storage using a managed identity and the Storage Blob Data Reader role.

Securing and managing access for Azure Storage

Azure Storage offers highly available, massively scalable, and durable storage for a variety of different data objects in the cloud. You can access this data from anywhere in the world over HTTPS via REST, or through client libraries using .NET, Python, Java, Node.js, and Go. Azure Storage platform includes Blob data, which acts as a object store for text and binary data, Azure Files for file shares for cloud or on-prem deployments, Elastic Storage Area Network (SAN) data, Azure Queues, Azure Tables, managed disks, and more! ...
November 7, 2026 · 7 min · Will Velida
Last week in Agent Security Update 2: Zam-mad Max

Configuring and Securing Azure Key Vault for the Enterprise

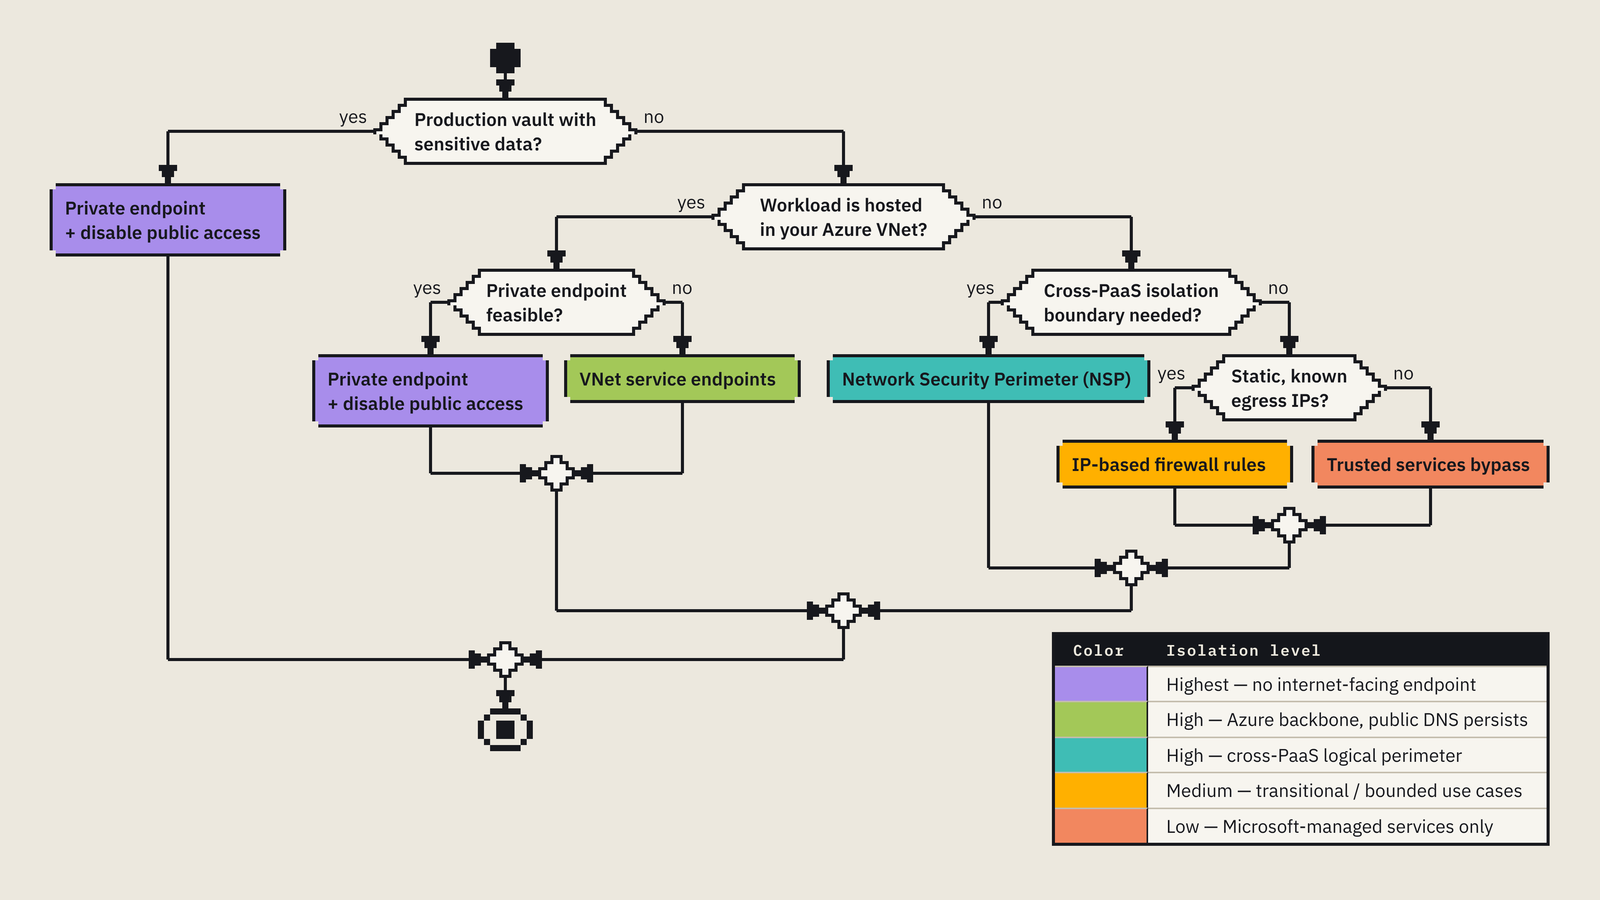
We can use Azure Key Vault to securely store and control access to sensitive information. We can use it to handle secrets (things like database connection string, passwords, API tokens etc.), cryptographic keys (used for encrypting and decrypting data), and certificates (SSL/TLS certificates used to secure communications). However, just having a Key Vault by itself doesn’t automatically make your application secure. We can deploy Azure Key Vaults with soft delete and purge protections to protect our vaults from accidental deletions, we can configure RBAC-based access controls, just-in-time activations using PIM, and we can lock down our Key Vaults using firewall rules, virtual networks, and private endpoints. ...

November 4, 2026 · 11 min · Will Velida
Last week in Agent Security Update 2: Zam-mad Max

Implement and configure Privileged Identity Management (PIM)

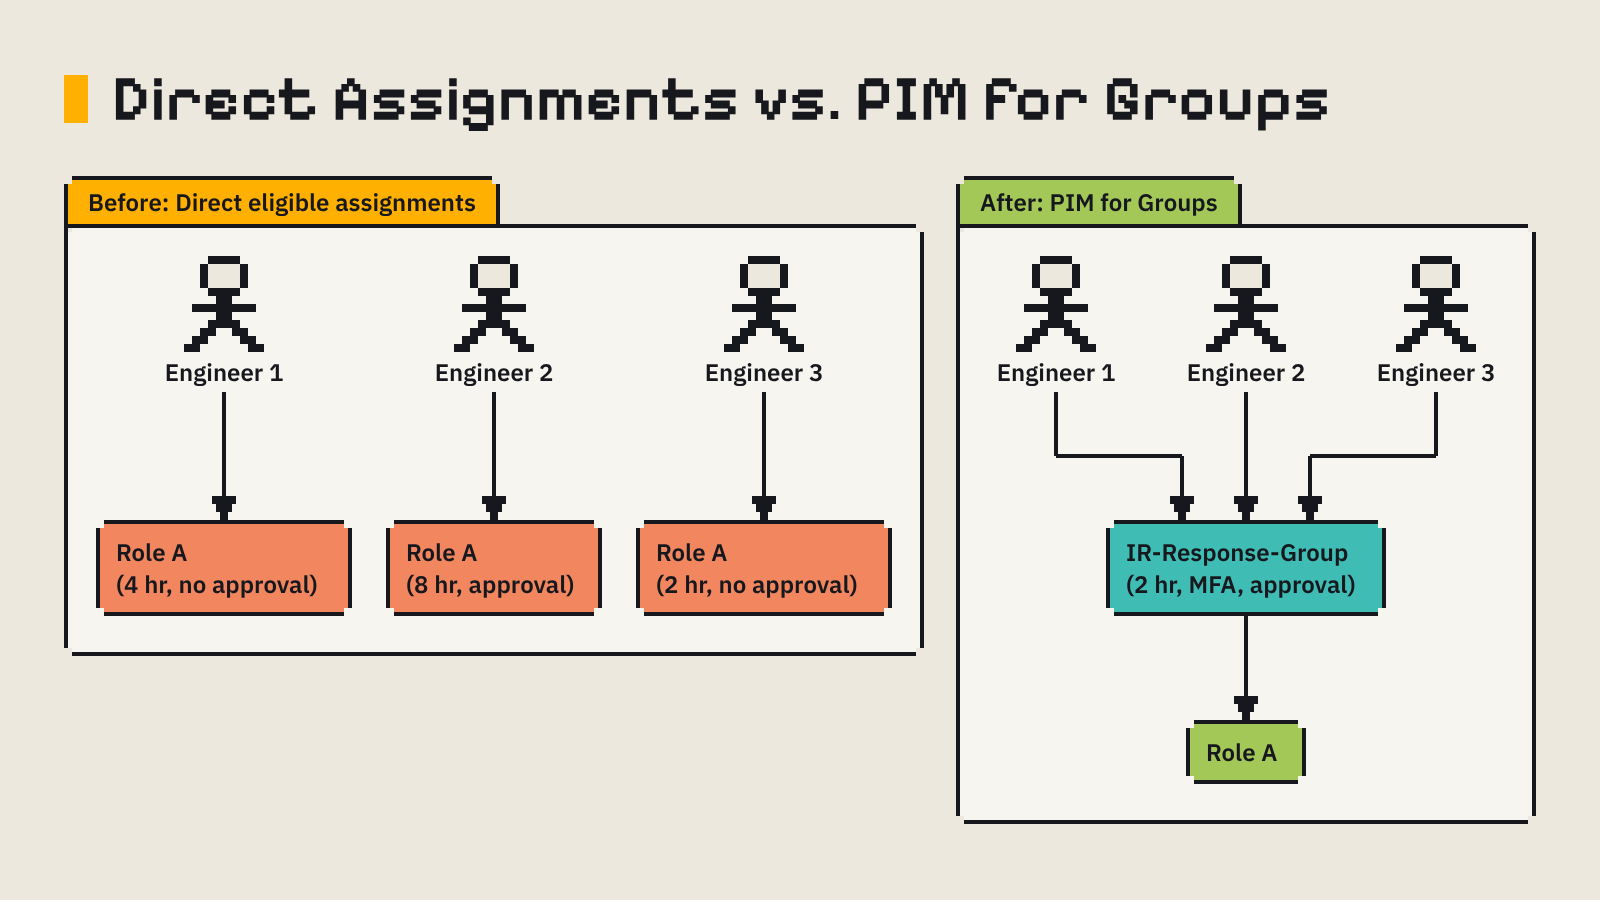
Imagine if an attacker was able to compromise a privileged user at your company. The damage they could do with that identity could have permanent effects and they can continue to do that damage until someone notices. This is was Privileged Identity Management, or PIM, is designed to stop. With PIM, we can implement just-in-time (JIT) access across a full surface of privileged access in a Microsoft cloud environment. Why does this matter? If you’ve ever worked on a greenfield project before, you’ve probably configured a Global Administrator account just to make sure you weren’t blocked when you needed to do administrative tasks. ...

November 3, 2026 · 8 min · Will Velida
Last week in Agent Security Update 2: Zam-mad Max

Manage and Implement authentication methods in Microsoft Entra ID

Microsoft Entra ID supports a wide range of authentication methods, from legacy password-based approaches to passwordless alternatives. These methods fall into the following categories: Something you know such as a password or PIN. Something you have such as a registered device, security key, or authenticator app. Something you are such as Biometric data, including fingerprints or facial recognition. Ideally, passwordless methods would be implemented since they remove the need for a password entirely. Instead, we can authenticate users using a combination of device possession and a biometric or PIN. ...

November 3, 2026 · 7 min · Will Velida
Distributed tracing for multi-agent systems with OpenTelemetry

Distributed tracing for multi-agent systems with OpenTelemetry

Multi-agentic architectures can pose challenges from an observability perspective. Each agent within a workflow makes its calls to its own toolset and each agent may be configured to use a different underlying LLM (or even a Model Router which picks the most efficient model for us). Being able to observe which agent made what call with which model in a unified manner can be challenging over an entire workflow. OpenTelemetry provides semantic conventions that help us solve this problem and Microsoft Foundry provides tracing integrations for agent frameworks that enable us to implement tracing for different agentic frameworks, and assist us in quickly identifying root causes for issues in our agents. ...

August 5, 2026 · 12 min · Will Velida